
Technology News
Major Lapse: Trump’s Acting Cyber Chief Allegedly Uploaded Sensitive Government Files To ChatGPT

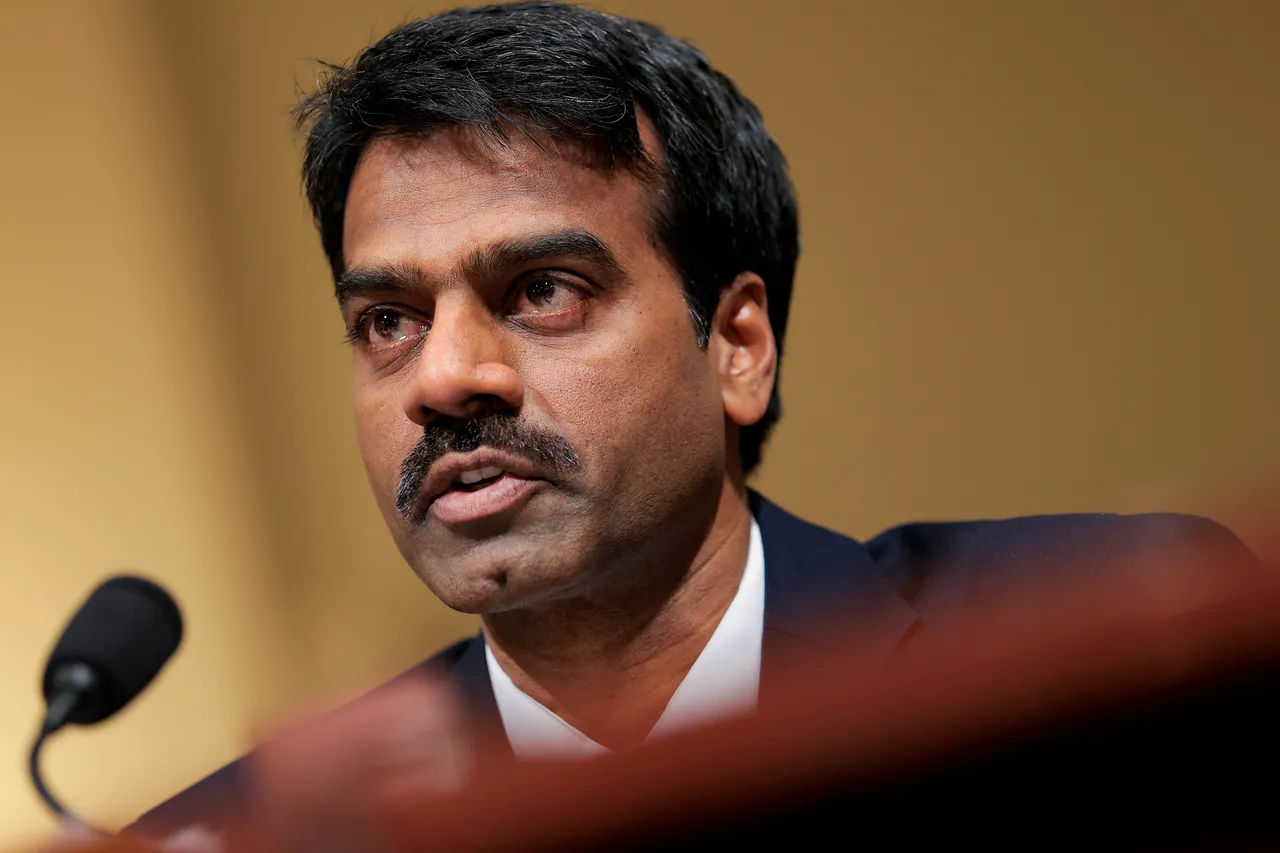
The acting head of the U.S. Cybersecurity and Infrastructure Security Agency (CISA) is under scrutiny for reportedly uploading sensitive “For Official Use Only” government documents to public AI platforms, including ChatGPT. The alleged actions bypassed standard security protocols and automated alerts, creating a potential risk of unauthorized data exposure.
Security Alerts Triggered
Reports indicate that the official’s actions prompted multiple warnings from the government’s automated security systems, which are designed to prevent accidental or malicious leaks of sensitive files. While the acting chief was reportedly allowed limited use of ChatGPT, other staff members were restricted from sharing documents on the platform.
Risk of Data Exposure
Uploading internal documents to large language models (LLMs) carries significant cybersecurity risks. AI platforms can retain and learn from user-submitted data, raising the possibility that confidential information could appear in responses to other users. Even files considered “unclassified” may contain operational details that must remain confidential under government policy.
Previous Controversies and Internal Action
The official’s appointment dates back to the Trump administration. Earlier reports indicated a failed counterintelligence polygraph test, later invalidated by the Department of Homeland Security. Following the incident, six staff members under the official’s supervision were suspended from accessing classified information.
CISA Statement
A CISA spokesperson stated that the official’s ChatGPT usage was limited in scope and duration. The Department of Homeland Security is conducting an investigation to determine the extent of any potential damage caused by the uploads.
Expert Warnings on AI and Sensitive Data
Cybersecurity experts stress that both government officials and private users should exercise extreme caution when uploading sensitive documents—including financial records, medical files, identification documents, or legal agreements—to AI platforms. AI providers often review chat data to improve system performance, which could inadvertently expose confidential information. Once incorporated into AI models, sensitive data may also resurface in responses to unrelated queries.
The incident highlights the ongoing challenges of integrating AI tools in secure environments, emphasizing the need for strict protocols and awareness of potential risks.
Artificial Intelligence
Are Smart Glasses Becoming a Privacy Threat? Norway Considers Major Restrictions
Norway is considering restrictions, including a possible ban, on smart glasses and other wearable devices equipped with cameras and internet connectivity amid growing concerns over privacy and surveillance.
The devices can capture images and videos, connect to the internet and may increasingly incorporate artificial intelligence-powered features such as facial recognition.
What Has Prompted Norway to Consider Restrictions?
Norway’s Digital Minister Karianne Tung has said the government is examining new regulations to control the use of camera-enabled wearable devices. The proposed measures could cover smart glasses made by companies such as Meta and Snap. Civil liberties and privacy advocates have raised concerns that the technology could allow people to be recorded without their knowledge or consent.
Why Is Norway Considering a Ban on Smart Glasses?
The government is concerned that camera-enabled smart glasses can record people discreetly in public places. Unlike smartphones, which are generally visible when someone is taking a photo or recording video, smart glasses can resemble ordinary eyewear and may make it difficult for people nearby to know that they are being recorded.
The concern becomes more serious when cameras are combined with microphones, internet connectivity and artificial intelligence. Such devices could potentially collect, process and transmit personal information in real time, raising questions about consent, surveillance and misuse.
A possible ban or tighter restrictions would therefore be aimed at preventing covert recording, unauthorised facial recognition and continuous monitoring of people in public spaces.
What Privacy Risks Do Camera-Enabled Wearables Create?
According to the government, smart glasses and other camera-enabled wearables present a distinct privacy challenge because they can be used discreetly in public spaces. A person wearing such a device could potentially record photographs or videos of people nearby without making it obvious that a camera is operating.
As the devices are connected to the internet, captured material could also be transmitted to other devices or online services.
Tung said there was a clear trend towards combining artificial intelligence with cameras and microphones embedded in everyday objects. She pointed to glasses, headphones, hats and other wearable items as examples of products where such technology is increasingly being integrated.
Could Facial Recognition Become a Major Concern?
The minister said the government must prevent these devices from being used to monitor other people in public places. Possible regulations could also include restrictions on using facial recognition technology to identify individuals in public spaces.
Technology experts have warned that combining cameras and microphones with artificial intelligence could significantly increase the amount of information such devices can collect and process.
If facial recognition becomes widely available on wearable devices, they could potentially be used to identify people in public places, monitor their movements and gather information about their activities.
How Could Norway Regulate Smart Glasses?
Norway plans to establish a group of experts to advise the government on ways to strengthen privacy protections. The objective is not necessarily to stop the development of wearable technology, but to establish safeguards against the risks that could emerge as such devices become more capable and widely used.
Future rules could establish clearer limits on recording people in public places, using camera-enabled wearables and deploying facial recognition technology.
The proposed restrictions could apply to smart glasses developed by major technology companies, including Meta and Snap, depending on the capabilities of the devices and how they are used.
Why Are Smart Glasses Becoming a Global Privacy Debate?
Technology companies are increasingly positioning smart glasses as a possible alternative or complement to smartphones. These devices are designed to provide hands-free access to digital services while allowing users to interact with technology without constantly using a phone.
However, their growing capabilities have raised difficult questions about how to balance convenience with individual privacy. A person using ordinary-looking glasses may potentially record others without attracting attention, making consent and transparency harder to enforce.
Norway’s move reflects a broader international debate over privacy as artificial intelligence, cameras, microphones and wearable technology become increasingly integrated.
What Should Smart Glasses Users Keep in Mind?
Consumers using camera-enabled wearables should respect local privacy laws, avoid recording people without their knowledge where consent is required, and use facial recognition or similar features cautiously. As governments consider tighter rules, users should also stay aware of changing regulations before using such devices in public spaces.
Japan is preparing to use generative artificial intelligence to detect investment fraud earlier, with the country’s Consumer Affairs Agency planning to analyse thousands of complaints for warning signs of suspicious schemes promising high returns.
How will Japan use AI to fight investment fraud?
The Consumer Affairs Agency said it will strengthen efforts against investment and other fraud promising lucrative returns by using generative AI to improve information analysis.
A new group established within the agency will use the technology to identify schemes that share patterns with previous fraud cases and malicious business operators. The aim is to spot potentially harmful operations earlier and allow authorities to intervene before losses grow.
What types of investment schemes will be targeted?
The agency announced measures against schemes that attract large amounts of money by promising high returns before eventually collapsing.
The AI-based approach will examine similarities between newly reported cases and past fraudulent schemes. By identifying recurring characteristics, authorities hope to recognise suspicious operations before they cause wider financial damage.
Why does Japan want to detect these schemes earlier?
Consumer Affairs Minister Hitoshi Kikawada stressed that recovering money can become difficult after victims have already suffered losses.
“Once damage occurs, it will be difficult to recover, so it is important to respond quickly,” Kikawada told a press conference.
The initiative is therefore focused on identifying warning signs at an earlier stage rather than relying only on action after consumers have already lost money.
How many consumer cases will the AI analyse?
The new group will operate a generative AI system to analyse cases reported to the National Consumer Affairs Center’s information system for consultation.
The system receives around 900,000 cases annually, giving authorities a large pool of consumer reports that can be examined for recurring fraud patterns and suspicious activity.
What warning signs will the system look for?
The AI system is designed to identify suspicious schemes and detect early signs that a business could fail.
It will analyse distinctive solicitation phrases and other characteristics extracted from previously reported cases. These indicators can then be compared with newer complaints to help authorities identify possible risks.
What could the AI system change for consumers?
The initiative is intended to help authorities move faster when similar fraud patterns begin appearing in consumer complaints. Earlier identification could give officials an opportunity to examine suspicious schemes before they expand and cause larger losses.
For consumers, the development also highlights the importance of caution when approached with investment opportunities promising unusually attractive returns. Suspicious offers should be examined carefully, particularly when they resemble schemes built around promises of high returns before eventually collapsing.
About the author — Ayesha Aayat writes on cybercrime, digital safety, and emerging online threats. Her work focuses on public awareness, legal clarity, and technology-driven risks.
Hyderabad Cybercrime Police have issued a notice to Meta seeking details about how its platforms detect and remove artificial intelligence-generated deepfake videos being used to promote fraudulent investment schemes.
The investigation follows a growing number of complaints from victims who say they were tricked by manipulated videos featuring well-known public figures allegedly endorsing fake trading platforms and investment opportunities. Authorities are examining how such content spreads across Facebook, WhatsApp, and Instagram and whether additional safeguards are needed to prevent financial fraud.
Fake Celebrity Videos Used to Lure Investors
Investigators have identified multiple cases where deepfake videos allegedly showed prominent personalities appearing to support fake financial schemes.
The probe includes manipulated content featuring Union Finance Minister Nirmala Sitharaman, actor Amitabh Bachchan, and Hyderabad MP Asaduddin Owaisi. Police said these videos were circulated online to create false credibility and encourage users to invest money through fraudulent platforms.
Owaisi had earlier approached Hyderabad Police after his identity was allegedly misused in a fake investment promotion. Similar deepfake-based scams have also targeted other public figures, including business leaders and celebrities, as fraudsters increasingly use trusted faces and voices to convince victims.
Fraud Pattern Follows a Common Method
Cybercrime investigators said many investment scams follow a similar approach. Criminals first use deepfake videos or fake advertisements to attract victims, then move conversations to private messaging platforms such as WhatsApp or Telegram.
Victims are often shown fake trading dashboards displaying artificial profits. When they attempt to withdraw funds, scammers demand additional payments in the form of taxes, processing charges, or verification fees.
Authorities have warned that the realistic appearance of AI-generated videos makes these scams more difficult for ordinary users to identify.
Meta Asked to Explain Detection Measures
A Meta representative has already appeared before investigators, who presented details of cases involving significant financial losses. Police have now requested technical experts from the company to explain the systems used to identify, monitor, and remove AI-generated fraudulent content.
The investigation reflects a broader effort by Telangana cybercrime authorities to examine the responsibilities of major technology platforms in preventing online fraud.
Officials are also reviewing whether social media companies and digital platforms are taking sufficient preventive measures rather than responding only after victims report losses.
Growing Pressure on Technology Platforms
The action against Meta follows similar scrutiny of other technology companies. In a separate investigation, Cyberabad Police questioned processes related to fraudulent stock-trading applications that allegedly caused financial losses after appearing on an app marketplace.
Together, these cases indicate a stronger focus by law enforcement agencies on the role of digital platforms in enabling cybercrime through advertisements, applications, and user-generated content.
Authorities are also examining the impact of updated Indian technology regulations that increase obligations for online platforms regarding synthetic media, harmful content detection, and user safety.
Experts Warn of Rising AI Fraud Threat
Cybersecurity experts have described AI-generated deepfakes as one of the fastest-growing threats in the online fraud landscape.
Experts warn that criminals can now create convincing videos and voice recordings of trusted individuals, making victims more likely to believe false investment claims.
Authorities have advised users to verify investment opportunities through official sources, avoid transferring money based solely on online promotions, and remain cautious of offers promising unusually high returns.
Investigation Continues
Hyderabad Cybercrime Police said the investigation will focus not only on identifying scam operators but also on understanding how fraudulent content reaches large audiences.
Officials believe cooperation between law enforcement agencies and major technology companies will be essential to reducing organized cyber fraud and improving digital safety for users.
-
 Business3 years ago
Pot Odor Does Not Justify Probable Cause for Vehicle Searches, Minnesota Court Affirms
-
 Business3 years ago
New Mexico cannabis operator fined, loses license for alleged BioTrack fraud
-
 Business3 years ago
Alabama to make another attempt Dec. 1 to award medical cannabis licenses
-
 Business3 years ago
Washington State Pays Out $9.4 Million in Refunds Relating to Drug Convictions
-
 Business3 years ago
Marijuana companies suing US attorney general in federal prohibition challenge
-
 Business3 years ago
Legal Marijuana Handed A Nothing Burger From NY State
-
 Business3 years ago
Can Cannabis Help Seasonal Depression
-
 Blogs3 years ago
Cannabis Art Is Flourishing On Etsy