
Technology
India–EU Tech Pact Lays Roadmap to 2030 ‘Digital Superpower’ Ambition

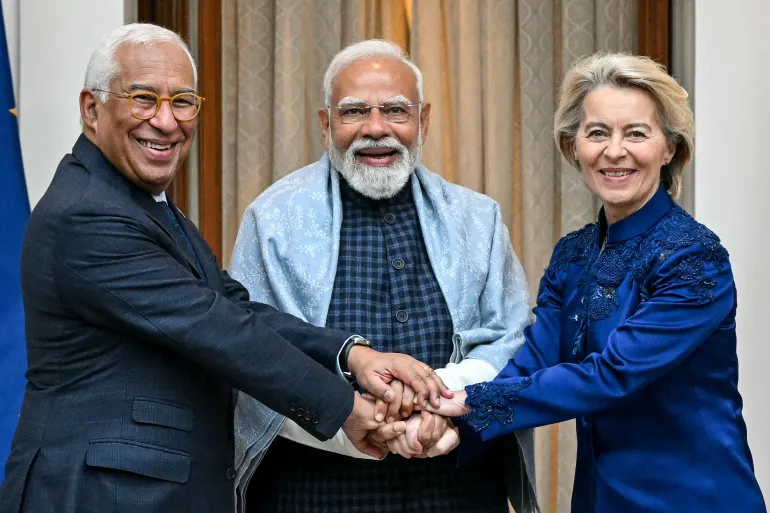
New Delhi / Brussels: India and the European Union have unveiled a landmark technology partnership under the “Towards 2030” agenda, aimed at positioning India as a global digital and technology hub by the end of the decade. The pact emphasizes semiconductors, artificial intelligence (AI), quantum computing, 6G communications, and secure digital infrastructure, reflecting deepening economic and technological cooperation.
Technology and Innovation at the Centre
The agreement prioritizes joint collaboration in next-generation technologies. Key focus areas include:
- Semiconductors: Research, manufacturing, and resilient supply chains to support economic growth and national security.
- AI and Quantum Computing: Shared research and development, with a focus on interoperability, safety, and ethical usage.
- 6G and Future Telecom Standards: Development of secure, interoperable communications systems.
Europe has also shown interest in adopting aspects of India’s digital public infrastructure, including large-scale platforms for identity, payments, and service delivery. This is expected to strengthen trusted digital ecosystems and highlight India’s technological capabilities on the global stage.
Reducing Strategic Dependence
The pact aims to diversify technology supply chains and reduce reliance on a single geography, ensuring access to trusted components, platforms, and standards. Collaboration will also cover cybersecurity, secure communications, and defense-related technologies, aligning European expertise with India’s manufacturing and innovation capacity. The goal is to protect critical infrastructure while boosting domestic technological self-reliance.
Opportunities for Talent and Businesses
The agreement extends beyond government collaboration to benefit professionals, startups, and businesses:
- Skills Development and Talent Mobility: Easier pathways for Indian researchers, entrepreneurs, and skilled workers to engage in Europe.
- Innovation Partnerships: Joint R&D projects to expand cross-border business and research opportunities.
- Startups and Industry Collaboration: European firms gain access to India’s technology workforce, while Indian companies gain global exposure.
Next Steps on the Global Stage
The next India-EU Trade and Technology Council meeting, scheduled for 2026 in Brussels, will review progress and explore additional areas for cooperation. Officials see the pact as a platform for aligning standards, regulations, and policy frameworks in emerging technologies.
Analysts note that, if effectively implemented, the roadmap could strengthen India’s role in global tech value chains, expand domestic manufacturing, and accelerate its ambition of becoming a leading digital and innovation powerhouse by 2030.
AI & Technology
Google Unveils Fairwind: Next-Gen AI Defense to Shield Critical Infrastructure from Cyber Threats
Google has introduced its Fairwind Cybersecurity Program to provide advanced cybersecurity support to government entities, Google Cloud customers and partner organizations, with a focus on identifying, addressing and mitigating cyber threats.
What Is Google’s Fairwind Cybersecurity Program?
The program is designed to help organizations respond to evolving cyber threats, including automated attacks, software vulnerabilities and increasingly sophisticated threat actors. Google said the initiative will provide access to advanced artificial intelligence capabilities to assist security teams in detecting and responding to threats more efficiently.
The focus extends across both public and private organizations, with the aim of strengthening their ability to protect digital infrastructure from cyberattacks.
How Will Fairwind Help Organizations Tackle Cyber Threats?
A key component of Fairwind is access to Google’s Gemini AI models. The models are intended to support cybersecurity operations and help organizations proactively defend their information technology infrastructure.
Security teams can use AI capabilities to analyze large volumes of data, identify potential weaknesses and respond to emerging threats more quickly. The program could be particularly relevant for government agencies and critical infrastructure operators, where cyberattacks could disrupt essential services and expose sensitive information.
How Will Gemini AI Support Cybersecurity Operations?
Fairwind is also expected to focus on identifying and fixing vulnerabilities across public and private organizations. Instead of relying only on traditional, reactive cybersecurity measures, the initiative emphasizes prevention and continuous protection.
The approach is intended to help participating organizations identify vulnerabilities before they can be exploited by malicious actors, strengthening their overall security posture.
What Technologies Will Google Use Under Fairwind?
According to the program’s planned capabilities, Fairwind will incorporate Gemini 3.8 Flash Cyber along with CodeMender Harness to support vulnerability remediation at what Google describes as an agentic scale.
These capabilities are intended to automate parts of the vulnerability-patching process, potentially allowing organizations to address security weaknesses more quickly and efficiently.
Google Announces Wider Cybersecurity Investment
Alongside the Fairwind announcement, Google has released its U.S. Cybersecurity Impact Report, outlining the company’s broader investments in cybersecurity. The report details a $100 million global cybersecurity initiative aimed at improving cyber resilience among organizations and communities.
As part of this investment, approximately $36 million has been allocated to 35 cyber clinics. These clinics are intended to provide cybersecurity assistance to organizations that may have limited resources while facing significant cyber risks.
Which Organizations Will Benefit From Google’s Cybersecurity Support?
The cyber clinics are expected to support organizations in responding to cyber risks, including helping healthcare organizations recover from cyberattacks and assisting municipal utilities in strengthening their defenses against sophisticated threats, including state-sponsored threats.
Google’s broader cybersecurity efforts reflect the growing importance of cooperation between technology companies, governments and other organizations as digital systems become increasingly important to healthcare, utilities, public administration and other essential services.
With the Fairwind Cybersecurity Program and its wider cybersecurity investments, Google is combining artificial intelligence, automated vulnerability remediation and direct support for organizations as part of a more proactive approach to cyber defense.
The Road Ahead
As cyber threats become faster and more automated, manual security responses simply can’t keep up. Google’s fusion of agentic AI patching and direct community support offers a glimpse into the future of digital defense—where threats are stopped before they ever cause damage.
Police in Madhya Pradesh’s Indore have busted a cyber fraud network allegedly operating through the buying and selling of SIM cards. The investigation revealed that one SIM card was passed from its registered holder to several other people for money before eventually being used in cyber fraud. Police have arrested Rajesh Chaudhary, 42, in connection with the case and are searching for Bhagwandas alias Nana, Himanshu Junwal and Ashish Sharma.
How Did 151 SIM Cards Get Linked to 212 Fraud Complaints?
The case came to light during verification of suspicious data received from the Indian Cyber Crime Coordination Centre. Police found that 151 suspicious SIM cards linked to 49 point-of-sale holders and SIM-selling agents in the Indore urban area had been used in 212 financial fraud complaints registered across different states and cities.
Following the finding, investigators began examining the suspected numbers, their registered holders and the people involved in issuing and transferring the SIM cards.
During the investigation, one suspicious SIM was traced to Rohit Dalve, 27, a resident of Swarnbag Colony. During questioning, Dalve told investigators that he had issued the SIM on March 15, 2026, after completing the required document verification.
The SIM was issued in the name of Rajesh Chaudhary, 42, of Indore. Police subsequently questioned Chaudhary, leading investigators to uncover the chain through which the SIM allegedly changed hands.
How Did One SIM Pass Through Multiple Hands?
According to police, Chaudhary had obtained the SIM using his Aadhaar card but later handed it over to Bhagwandas alias Nana for ₹200.
Bhagwandas allegedly passed the SIM to Himanshu Junwal for financial gain and received around ₹500 in return. Investigators found that Junwal subsequently handed the same SIM to Ashish Sharma, who allegedly used the number for cyber fraud.
The investigation therefore revealed a chain in which the SIM moved from its registered holder to several individuals in exchange for money before reaching the alleged fraudster.
Such repeated transfers can make it difficult for investigators to immediately establish the identity of the person actually operating a SIM during a cybercrime.
How Were Victims Allegedly Trapped With Clothing and Franchise Offers?
Investigators found that the suspicious number was allegedly used to contact people with offers of jeans and pants at wholesale prices.
The accused allegedly collected money from customers but failed to supply the promised goods. In another method, victims were allegedly offered franchises for wholesale clothing businesses and asked to make payments.
The case was also linked to a complaint filed by Anil Kumar Gupta, a resident of Kheri district in Uttar Pradesh. According to the complaint, the accused allegedly offered him a franchise for a wholesale jeans and pants business.
They allegedly demanded ₹30,000 for the franchise and collected ₹10,000 from him as part of the deal. However, neither the promised franchise nor the goods were provided. Gupta subsequently filed a complaint on the National Cyber Crime Reporting Portal on May 27, 2026.
Who Has Been Arrested and Who Is Still Being Searched For?
Based on the complaint and findings from the investigation, MIG police registered a case and initiated further action.
Rajesh Chaudhary has been arrested, while Bhagwandas alias Nana, Himanshu Junwal and Ashish Sharma remain absconding.
Police are now examining the roles allegedly played by each person in obtaining, transferring and ultimately using the SIM card.
Is There a Bigger SIM Network Behind the Cyber Frauds?
Investigators are examining whether the 151 suspicious SIM cards linked to 212 financial fraud complaints were operated by a single organised network or were being used by multiple cybercrime groups.
Police are also looking into the wider network involved in the transfer and misuse of SIM cards, including the role of point-of-sale holders and SIM-selling agents linked to the suspicious numbers.
The case highlights the risks associated with SIM cards being obtained in one person’s name and subsequently handed over to others for money. Users should never sell, rent or hand over SIM cards registered in their name, as misuse of the number in cybercrime can bring the registered subscriber under investigation while making it harder for police to identify the actual fraudster.
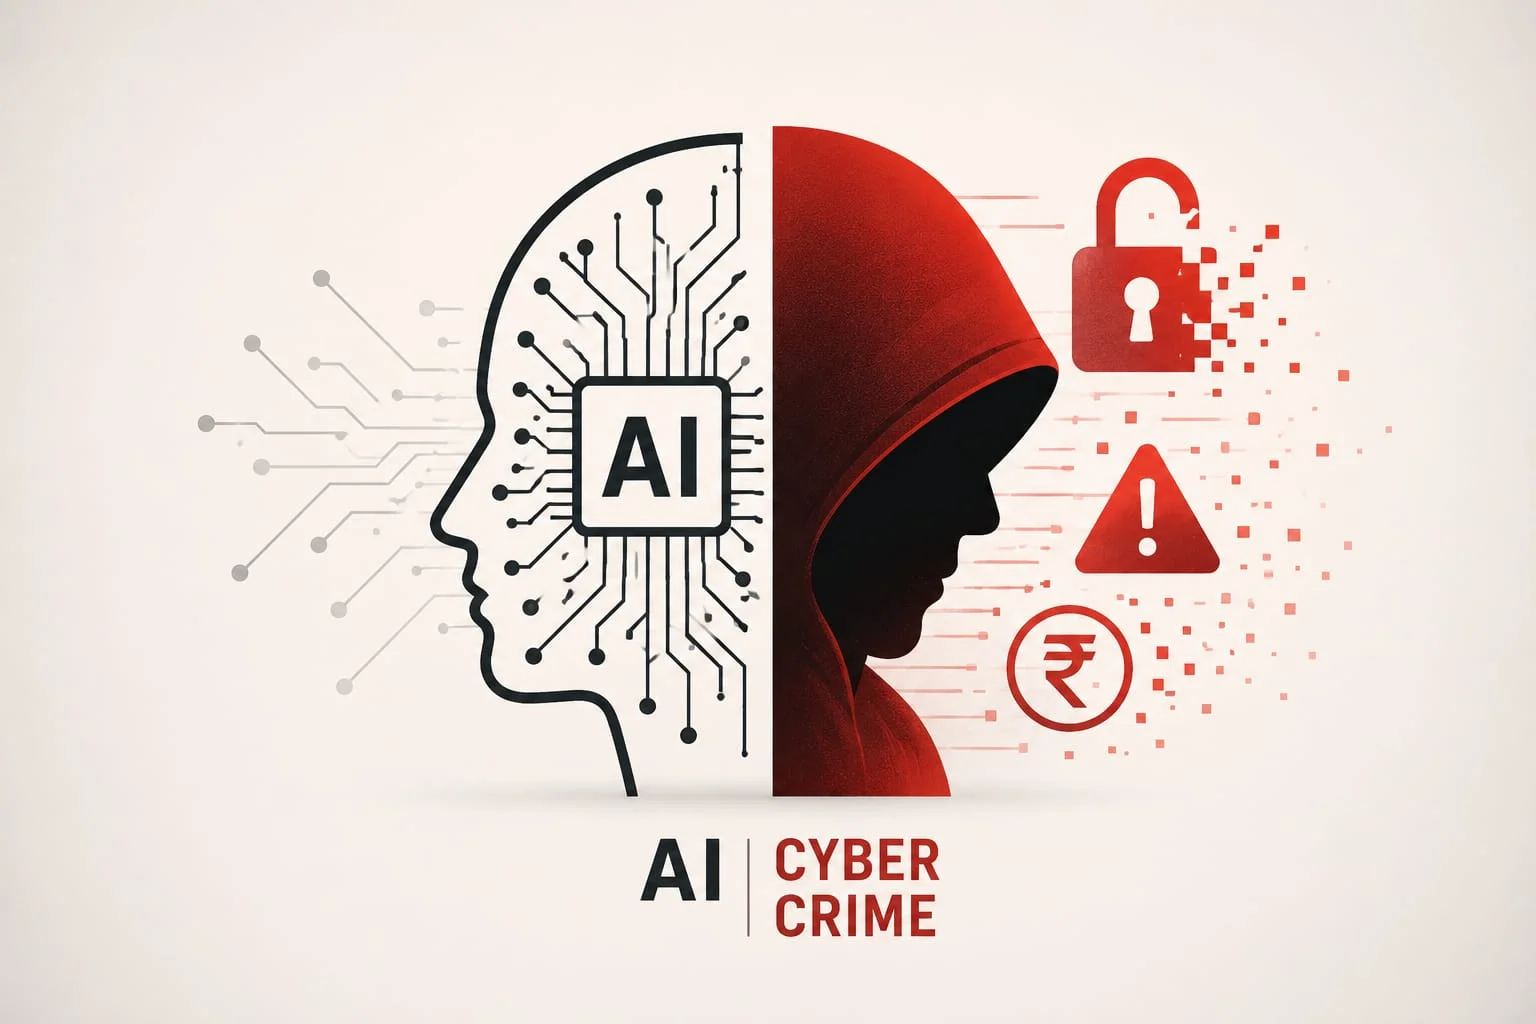
Artificial intelligence is giving cybercriminals new ways to make financial scams appear genuine, from cloned voices and deepfake videos to highly personalised phishing messages and synthetic identities.
Traditional fraud often relied on generic emails, suspicious links or poorly written messages. AI is changing that approach by allowing scammers to create convincing communications tailored to individual victims.
The growing availability of generative AI has also lowered the technical barrier for producing fake audio, video, documents and identities, creating new challenges for consumers, businesses and financial institutions.
What Are AI-Powered Financial Scams?
AI-powered scams use technologies such as machine learning, natural language processing and generative AI to make fraudulent activity more convincing and scalable.
Criminals can use AI to analyse publicly available information and create messages that appear relevant to a particular person. Social media profiles, leaked information and other online data can potentially be used to understand a target’s relationships, interests or professional background.
AI can then help produce personalised messages, realistic conversations and convincing fake content designed to gain a victim’s trust.
The result is a shift from broad, mass-targeted scams toward fraud attempts that can appear specifically designed for one individual.
How Are Cybercriminals Using AI to Target Victims?
One emerging tactic involves AI-powered chatbots and automated systems that can maintain realistic conversations with potential victims.
Voice-cloning technology presents another serious threat. With a relatively small amount of audio, criminals can potentially reproduce characteristics of a person’s voice and use the result in fraudulent phone calls.
A scammer could, for example, impersonate a family member, company executive or other trusted individual and create a sense of urgency before requesting money or sensitive information.
AI can also help criminals process large amounts of stolen or leaked data. Instead of manually researching individual targets, automated systems can potentially identify people who may be more likely to respond to particular types of scams.
This automation allows fraud campaigns to operate on a much larger scale.
What Are the Most Common Types of AI-Driven Fraud?
Several forms of AI-assisted fraud are becoming increasingly prominent.
Deepfake Video Scams
Deepfake technology can be used to create convincing videos that imitate the appearance and voice of another person.
Criminals may attempt to impersonate executives, government officials, financial professionals or even family members to persuade victims to transfer money or reveal confidential information.
AI-Generated Phishing
AI can produce polished and personalised emails, text messages and other communications without the grammatical mistakes traditionally associated with many phishing attempts.
A fraudulent message can potentially reference a person’s workplace, recent activities or other contextual information to make the request appear legitimate.
Voice-Cloning Fraud
Voice cloning can be used to imitate someone familiar to the victim.
Scammers may create fake emergency situations involving relatives or impersonate bank representatives requesting sensitive information such as one-time passwords or account details.
Synthetic Identity Fraud
Synthetic identity fraud combines genuine information with fabricated details to create identities that may appear legitimate.
Such identities can potentially be used to open financial accounts, obtain credit or carry out other fraudulent activities while making it harder for investigators to determine who is behind the operation.
How Convincing Can AI Impersonation Become?
AI-generated audio and video can reproduce characteristics such as a person’s voice, appearance, accent and speaking style with increasing realism.
That makes it possible for scammers to create communications that appear to come from a boss, colleague, family member or financial institution.
The danger increases when the impersonation is combined with pressure.
A victim may receive what appears to be an urgent call from a familiar person asking for an immediate transfer or confidential information. Under pressure, the victim may focus on responding quickly instead of verifying the request.
For this reason, a familiar face or voice should no longer be treated as conclusive proof of someone’s identity when money or sensitive information is involved.
How Can AI Fraud Affect Victims?
The consequences of AI-assisted fraud can extend well beyond the initial financial loss.
Victims may face unauthorised transactions, fraudulent accounts or loans opened using their information, identity-related problems and lengthy efforts to recover money or restore their financial records.
Businesses can also be targeted through executive impersonation and other forms of social engineering. A convincing fake communication appearing to come from a senior employee could potentially persuade staff to make an unauthorised payment or disclose confidential information.
The increasing sophistication of these attacks is also putting pressure on banks and financial institutions to strengthen fraud detection. Behavioural monitoring, transaction analysis and other security systems are increasingly important for identifying unusual activity.
How Can People Recognise an AI-Powered Scam?
AI-generated content can be convincing enough that users should not rely solely on appearance or sound when deciding whether a communication is genuine.
Several warning signs deserve attention:
- An unexpected request for money or sensitive information.
- Pressure to act immediately.
- Requests for OTPs, passwords, PINs or banking credentials.
- Unfamiliar links or attachments.
- A sudden request to change payment details.
- A video or voice call that seems unusual despite appearing authentic.
- Messages that discourage independent verification.
Even professionally written messages can be fraudulent. AI allows criminals to produce polished communications without the obvious spelling and grammar mistakes commonly associated with older phishing campaigns.
When a request involves money, users should independently verify the identity of the sender before taking action.
Real-World AI Fraud Shows the Growing Threat
Cases involving deepfake videos, voice cloning and AI-generated impersonation have demonstrated how criminals can exploit public trust.
Fake videos may be created to imitate public figures and promote fraudulent investment schemes, while cloned voices can be used to manufacture emergencies involving relatives or trusted contacts.
These cases highlight an important change in online fraud: convincing content can now be generated at scale, meaning users can no longer assume that realistic audio or video is genuine simply because it looks and sounds authentic.
How Can People Protect Themselves?
As AI-powered fraud becomes more sophisticated, independent verification is one of the most effective defences.
Users should:
- Verify unexpected requests: Contact the person or organisation through a trusted number or separate communication channel.
- Slow down when faced with urgency: Pressure is a common tactic used to prevent victims from checking a request.
- Never share financial credentials: Do not disclose OTPs, passwords, PINs or banking details to someone who contacts you unexpectedly.
- Treat links and attachments cautiously: Avoid clicking unfamiliar links, even when the message appears professionally written.
- Enable multi-factor authentication: Additional authentication can provide another layer of account protection.
- Limit personal information online: Public social media information can help criminals create more convincing impersonation attempts.
- Monitor financial accounts: Regularly review bank and payment activity for transactions you do not recognise.
- Verify voice and video calls: If someone makes an unusual financial request, contact them separately rather than relying on the original call.
The Biggest Lesson as AI Scams Evolve
The rise of AI-assisted fraud means that traditional warning signs are becoming less reliable. A message can be grammatically perfect, a voice can sound familiar and a video can look authentic while the underlying request is completely fraudulent.
The safest approach is therefore to verify before trusting.
Whenever a communication involves money, account access or confidential information, users should independently confirm the request—even when it appears to come from someone they know.
As artificial intelligence continues to advance, strong security practices, digital awareness and careful verification will become increasingly important tools for protecting personal and financial information.
-
 Business3 years ago
Pot Odor Does Not Justify Probable Cause for Vehicle Searches, Minnesota Court Affirms
-
 Business3 years ago
New Mexico cannabis operator fined, loses license for alleged BioTrack fraud
-
 Business3 years ago
Alabama to make another attempt Dec. 1 to award medical cannabis licenses
-
 Business3 years ago
Washington State Pays Out $9.4 Million in Refunds Relating to Drug Convictions
-
 Business3 years ago
Marijuana companies suing US attorney general in federal prohibition challenge
-
 Business3 years ago
Legal Marijuana Handed A Nothing Burger From NY State
-
 Business3 years ago
Can Cannabis Help Seasonal Depression
-
 Blogs3 years ago
Cannabis Art Is Flourishing On Etsy