
AICybercrime
I4C Flags Fake Adult Apps That Could Turn Android Phones Into Fraud Tools

Cyber fraud is no longer limited to phone calls, messages or fraudulent links. The Indian Cyber Crime Coordination Centre (I4C) has warned Android users about malicious applications being promoted on social media platforms such as Facebook and Instagram by disguising them as adult-content apps.
Users who click on these advertisements are redirected to external websites and persuaded to download APK files from outside the Google Play Store. Once installed, the apps can seek sensitive permissions and attempt to gain access to the device and personal information.
Which Fake Apps Has I4C Flagged?
The I4C, which operates under the Ministry of Home Affairs, has flagged suspicious applications operating under names such as “Night Play”, “Reloop”, “Kyss”, “Vimo”, “Rivo”, “Nexo” and “Vixa”, among others.
These apps are reportedly promoted through social media advertisements offering users access to adult content. Clicking on the advertisements takes users to websites where they are instructed to download an application to view the content.
How Does the APK Fraud Begin?
The fraud begins when users are persuaded to install an APK file from an external website instead of downloading an application through the Google Play Store. After installation, the malicious application may request access to sensitive functions such as notifications, messages or other device features. The risk becomes particularly serious when users grant an unfamiliar application access to Android’s Accessibility Services.
Why Is Accessibility Permission So Dangerous?
Accessibility Services is designed primarily to assist people who have difficulty operating touchscreen devices. However, cybercriminals can misuse this functionality. According to cybersecurity experts, a malicious application with Accessibility access may be able to read information displayed on the screen, interact with other applications and potentially approve certain permission requests on behalf of the user.
This creates a direct threat to banking and digital payment information. Smartphones often contain banking applications, UPI accounts, one-time passwords (OTPs), private messages and other sensitive information. If a malicious application gains extensive control over such a device, attackers may potentially exploit that access to facilitate financial fraud.
Some variants of the malware may also download another package by disguising it as an application update. In certain cases, the malicious software may install a VPN and attempt to route internet traffic through servers controlled by attackers. Such activity can further compromise the security and privacy of an affected device.
What Warning Signs Should Android Users Watch For?
Cybersecurity experts have advised users to pay close attention to unusual activity after installing an unfamiliar application. A phone appearing to tap or interact on its own, an unfamiliar VPN icon appearing on the device, or an unknown application showing up under Accessibility settings could be warning signs of a possible compromise.
Experts have also warned that users may be more likely to trust advertisements appearing on familiar social media platforms. However, being redirected from a legitimate platform to an external website and then being asked to install an APK significantly increases the security risk. Cybercriminals are increasingly targeting users before a financial transaction takes place, using deceptive advertisements and applications to gain access to devices and sensitive information.
The I4C has advised Android users to download applications only from the Google Play Store or other trusted app stores. Users should avoid APK files received through advertisements, websites or suspicious links. They should also keep Google Play Protect enabled, regularly update their Android devices and periodically review the applications installed on their phones.
Users should immediately review and remove applications they do not recognise and avoid granting Accessibility access to unfamiliar applications. Particular caution is required when an application asks users to enable unusual permissions or follow instructions to bypass normal installation procedures.
Users should also regularly monitor their bank accounts and UPI transactions for unauthorised activity. If someone suspects that their device has been infected with malware or notices an unauthorised financial transaction, they should immediately contact their bank and report the incident through India’s cybercrime helpline at 1930.
The threat also extends beyond personal smartphones. Employees may use the same devices for work email, banking and personal activities, potentially exposing organisational information to malicious applications. Companies should therefore consider restricting app installation from external sources on devices that access sensitive corporate data and maintain a response plan for suspected compromises.
The latest warning highlights a simple but critical cybersecurity rule: users should never install an unfamiliar application merely because an online advertisement promises free or exclusive content. Downloading apps from trusted sources and carefully reviewing requested permissions can significantly reduce the risk of handing control of a smartphone to cybercriminals.






Kerala Police have arrested a man at Hyderabad’s Rajiv Gandhi International Airport in connection with an alleged digital arrest scam in which an 80-year-old doctor from Kasaragod was reportedly defrauded of ₹1.19 crore.
The accused has been identified as Shamsad Choorakuth, a resident of Malattur in Malappuram. Police had issued a lookout circular after discovering that he had travelled abroad for employment.
Investigators allege that Choorakuth and his associates impersonated Mumbai Crime Branch officials and used threats of criminal action to pressure the elderly doctor into transferring large amounts of money.
Doctor Targeted Through Fake Mumbai Crime Branch Calls
According to investigators, the fraud took place between November 24 and December 17, 2025.
The victim, who lives in Nileswaram in Kasaragod, allegedly received repeated phone calls and WhatsApp video calls from people claiming to be Mumbai Crime Branch officers.
The callers reportedly told the doctor that his name had surfaced in a money-laundering investigation. They then falsely informed him that he was under “digital arrest” and instructed him to follow their directions.
The scammers allegedly maintained pressure on the victim by threatening him with legal consequences and claiming that transferring money to designated bank accounts would help establish his innocence.
Under the pressure, the doctor reportedly transferred a total of ₹1,19,35,000 from multiple bank accounts to accounts allegedly controlled by the fraudsters.
Suspect Intercepted at Hyderabad Airport
After receiving the doctor’s complaint, Kasaragod Cyber Police began investigating the financial transactions and communication records connected to the case.
During the investigation, police learned that Choorakuth had travelled outside India for work. Authorities subsequently issued a lookout circular covering immigration checkpoints.
On September 17, immigration officials at Rajiv Gandhi International Airport in Hyderabad reportedly intercepted Choorakuth after he arrived in the country and informed Kerala Police.
A cyber police team from Kasaragod travelled to Hyderabad and took custody of the suspect. Following his formal arrest, he was produced before the Kasaragod Chief Judicial Magistrate Court, which remanded him to 14 days of judicial custody.
Police Trace Money Trail and Other Suspects
Investigators are now examining the movement of the ₹1.19 crore allegedly transferred by the victim.
Police are scrutinising the bank accounts that received the funds and analysing communication records believed to connect the accused with other members of the suspected cybercrime network.
The investigation is aimed at determining Choorakuth’s specific role and identifying additional individuals who may have participated in the operation.
How Digital Arrest Scams Work
Digital arrest frauds typically rely on impersonation, intimidation and prolonged online interactions.
Scammers may pose as police officers, investigators, judges or other government officials and falsely accuse victims of involvement in serious crimes such as money laundering or financial fraud.
Victims are often told that they are under investigation or “digital arrest” and are instructed to remain connected through phone or video calls. The criminals then use threats of arrest, prosecution or account freezing to pressure victims into transferring money.
The Kasaragod case follows this pattern, with the elderly doctor allegedly being kept under sustained psychological pressure before transferring his savings.
Investigation Continues
The arrest at Hyderabad airport has provided investigators with an opportunity to examine the suspected financial and communication network behind the alleged fraud.
Authorities are expected to continue analysing bank transactions, digital communications and other evidence to identify the wider network and determine whether additional victims or financial accounts are connected to the case.
Kerala Police have arrested a man at Hyderabad’s Rajiv Gandhi International Airport over an alleged digital arrest scam in which an 80-year-old doctor from Kasaragod was reportedly cheated of ₹1.19 crore.
The accused, identified as Shamsad Choorakuth, a resident of Malattur in Malappuram, was intercepted by immigration officials after police issued a lookout circular against him. Investigators allege that he was part of a group that impersonated Mumbai Crime Branch officers to intimidate the elderly victim and extract money from him.
Fraudsters Claimed Doctor Was Linked to Money Laundering Case
The alleged fraud occurred between November 24 and December 17, 2025.
The doctor, who lives in Nileswaram, Kasaragod, reportedly received repeated phone calls and WhatsApp video calls from individuals claiming to represent the Mumbai Crime Branch.
The callers allegedly told him that his name had been connected to a money-laundering investigation. They then claimed that he had been placed under “digital arrest” and warned him of serious legal consequences.
Using these threats, the fraudsters allegedly instructed the victim to transfer money into several bank accounts as part of a supposed process to clear his name.
The doctor ultimately transferred ₹1,19,35,000 from multiple bank accounts to accounts allegedly controlled by the suspects.
Lookout Circular Leads to Airport Interception
After the victim reported the incident, Kasaragod Cyber Police began investigating the financial transactions and communications associated with the alleged fraud.
During the investigation, police reportedly discovered that Choorakuth had travelled overseas for employment. Authorities subsequently issued a lookout circular to immigration checkpoints.
On September 17, immigration officials at Hyderabad airport reportedly intercepted him after his arrival and notified Kerala Police.
A cybercrime team from Kasaragod then travelled to Hyderabad and took custody of the suspect. Following his arrest, Choorakuth was produced before the Kasaragod Chief Judicial Magistrate Court, which remanded him to 14 days of judicial custody.
Police Investigate Financial Trail
Investigators are now examining the movement of the ₹1.19 crore allegedly transferred by the victim.
Police are checking the bank accounts used in the transactions and analysing communication records to determine Choorakuth’s alleged links with other members of the suspected fraud network.
The investigation is also focused on establishing the accused’s precise role and identifying other people who may have been involved in the operation.
What Is a Digital Arrest Scam?
Digital arrest scams are a form of cyber fraud in which criminals impersonate police officers, government officials, investigators or judicial authorities.
Fraudsters typically tell victims that they are involved in a criminal investigation and use threats of arrest, prosecution or account restrictions to create fear.
Victims may be kept on prolonged phone or video calls while being instructed to transfer money to accounts controlled by the scammers.
In this case, investigators allege that the same tactic was used to convince the elderly doctor that he needed to transfer money to avoid criminal proceedings.
Investigation Into Wider Network Continues
The arrest at Hyderabad airport is now part of a wider investigation into the alleged cyber fraud network.
Police are expected to follow the financial trail and examine digital communications to identify additional suspects and determine whether other people were targeted using similar methods.
The case also highlights the growing use of impersonation and intimidation in online financial scams targeting elderly victims.
AICybercrime
ED Accuses IAS Officer Gyanendra Kumar Gangwar of Taking ₹1.30 Crore Bribe in KPSC Paper Leak
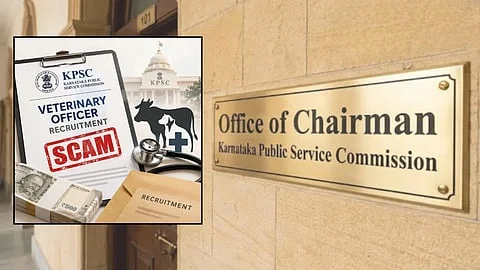
The Enforcement Directorate has alleged that suspended IAS officer Gyanendra Kumar Gangwar received ₹1.30 crore in cash from an alleged middleman in connection with the leakage of a Karnataka Public Service Commission (KPSC) Veterinary Officer recruitment examination paper.
The allegations were presented before a Bengaluru special court as the ED sought custody of Gangwar in a money-laundering investigation under the Prevention of Money Laundering Act (PMLA).
The court subsequently remanded Gangwar to six days of ED custody, until September 26, according to court reporting. The allegations remain subject to investigation and judicial proceedings.
ED Claims ₹1.50 Crore Was Collected From Candidates
According to the ED’s remand application, alleged middleman Basavaraj Kannale collected around ₹1.50 crore from candidates who were seeking access to the leaked examination material.
The agency alleges that approximately ₹1.30 crore of that amount was subsequently handed over to Gangwar in cash.
The ED is investigating the alleged flow of funds as part of its money-laundering probe and has sought to determine how the proceeds were collected, transferred and potentially converted into other assets.
Question Paper Allegedly Handed Over Before Examination
The ED has alleged that Gangwar provided the Veterinary Officer recruitment examination question paper, along with its answers, to Kannale through an HP pen drive on January 7, 2026.
The examination was scheduled for January 9.
Investigators allege that candidates who had paid money were subsequently given access to the examination material before the test. Earlier CID investigations have also examined allegations that selected candidates were taken to a resort and coached using leaked questions.
The recruitment examination was conducted for 400 Veterinary Officer posts in Karnataka.
Jewellery and Other Financial Transactions Under Investigation
The alleged financial trail also includes purchases of jewellery.
The ED told the court that approximately ₹23 lakh was spent on gold jewellery using funds connected to the alleged recruitment racket. Separate CID proceedings have examined additional jewellery purchases and other expenditures allegedly linked to the money collected from candidates.
Investigators are also examining financial transactions and other records to establish the full extent of the alleged money trail.
Gangwar Served as KPSC Examination Controller
Gangwar served as the Controller of Examinations at KPSC from 2024 until March 2026.
His role has brought particular attention to the alleged paper leak because investigators are examining how examination material could have been accessed and transferred before the test.
The ED is also investigating whether alleged proceeds from other recruitment examinations conducted during his tenure could be connected to the wider financial network.
Investigation Expands to Other KPSC Officials
The investigation is not limited to Gangwar and Kannale.
Authorities are examining the possible involvement of other individuals associated with the recruitment process, including suspended KPSC chairman Sahukar S. Shivashankarappa.
Investigators are looking into alleged communications, financial transactions and relationships between individuals involved in the recruitment process. The allegations against other officials remain under investigation and should not be treated as established findings.
Recruitment Process Came Under Scrutiny After Complaints
The alleged irregularities emerged after concerns were raised over the Veterinary Officer recruitment examination and selection process.
The CID investigation has examined allegations involving question-paper leakage, payments by candidates and the use of leaked material to prepare candidates before the examination. Earlier reporting said 329 candidates were selected from the recruitment process, while investigators were examining allegations involving candidates who allegedly paid money for selection.
The financial investigation by the ED is now focused on identifying the alleged proceeds of crime and tracing their movement.
High Court Orders Fresh Investigation
The wider KPSC controversy has also resulted in judicial intervention.
Recent reporting indicates that the Karnataka High Court constituted a Special Investigation Team (SIT) to conduct a fresh investigation into alleged irregularities connected with KPSC recruitment, including the Veterinary Officer examination.
The developments have expanded the case beyond the alleged paper leak to broader questions about recruitment procedures, financial transactions and the functioning of the commission.
ED Probe Continues
The six-day ED custody of Gangwar is intended to allow investigators to question him about the alleged financial transactions, identify other participants and trace the suspected proceeds of crime.
The case remains at the investigation stage. Allegations made by the ED or CID will ultimately have to be tested through the judicial process.
The KPSC controversy has meanwhile triggered wider scrutiny of recruitment examinations in Karnataka, with investigators continuing to examine whether the alleged network extended beyond the Veterinary Officer recruitment test.
-
 Business3 years ago
Pot Odor Does Not Justify Probable Cause for Vehicle Searches, Minnesota Court Affirms
-
 Business3 years ago
New Mexico cannabis operator fined, loses license for alleged BioTrack fraud
-
 Business3 years ago
Alabama to make another attempt Dec. 1 to award medical cannabis licenses
-
 Business3 years ago
Washington State Pays Out $9.4 Million in Refunds Relating to Drug Convictions
-
 Business3 years ago
Marijuana companies suing US attorney general in federal prohibition challenge
-
 Business3 years ago
Legal Marijuana Handed A Nothing Burger From NY State
-
 Business3 years ago
Can Cannabis Help Seasonal Depression
-
 Blogs3 years ago
Cannabis Art Is Flourishing On Etsy