
Cybersecurity
AI-Powered Cyber Threats Put India’s Financial Sector Under Growing Pressure, Report Warns


New security assessment highlights deepfakes, identity attacks, supply-chain risks and weaknesses beyond traditional compliance systems
India’s banking, financial services and insurance (BFSI) sector is facing a rapidly changing cyber threat environment as attackers increasingly use artificial intelligence, deepfake technology, identity manipulation and advanced digital techniques to target financial systems.
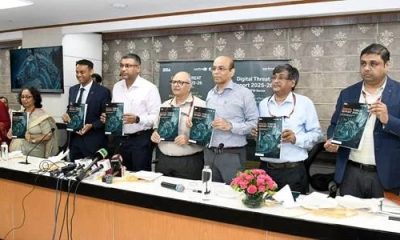
A new Digital Threat Report 2025-26 developed by SISA, CERT-In and CSIRT-Fin warns that cyber risks are evolving faster than many organisations can strengthen their defences. The report highlights that modern attacks are no longer limited to stealing information but are increasingly focused on disrupting transactions, compromising trust and exploiting digital infrastructure.
The assessment notes that several cyber trends predicted in the previous edition of the report have already become widespread, showing that the time between emerging threats and real-world attacks is becoming significantly shorter.
Deepfakes and AI Increase Sophistication of Financial Fraud
Artificial intelligence has become a major factor behind the growth of sophisticated cyber fraud campaigns. The report identifies AI-driven impersonation, deepfake videos, automated phishing and advanced social engineering as key challenges for financial institutions.
Criminal groups are increasingly using realistic fake identities, manipulated communications and AI-generated content to deceive employees and customers. Traditional verification methods based only on visual or voice recognition are becoming less reliable as attackers improve their ability to imitate trusted individuals.
The report also highlights rising risks from business email compromise, credential theft and session hijacking. Attackers are using stolen access details and legitimate user sessions to bypass security measures instead of directly breaking authentication systems.
Cyber incidents affecting India’s BFSI sector are estimated to be significantly higher than the global average, with reported incidents increasing substantially in recent years. The report stresses that organisations must focus on analysing user behaviour, device activity and transaction patterns rather than relying only on passwords or authentication checks.
Identity Protection Becomes a Critical Security Challenge
Cybercriminals are increasingly targeting digital identities after successful login attempts. The report warns that attackers are focusing on session tokens, application programming interface (API) keys, service accounts and cloud-based permissions.
In these situations, security systems may not detect a traditional authentication failure because attackers are operating through valid sessions or stolen credentials. Financial institutions are therefore being urged to strengthen identity monitoring and continuously review access privileges.
The report recommends improved management of non-human identities, stronger credential protection and better visibility into digital activity across applications and cloud environments.
Compliance Alone Cannot Guarantee Cyber Resilience
The report highlights a growing gap between meeting regulatory requirements and achieving real-world cybersecurity readiness.
While compliance frameworks help organisations establish security standards, they may not always reveal weaknesses that appear during active attacks. The report identifies issues such as outdated security practices, incomplete monitoring and gaps between designed controls and their actual operation.
For example, encryption may protect stored information but may not secure data while it is being processed. Multi-factor authentication can confirm identity but may not stop attackers who have already gained access through stolen sessions.
The report advises financial organisations to treat compliance as a starting point rather than a complete security solution. Continuous testing, threat simulations, behavioural monitoring and regular security reviews are recommended to strengthen resilience.
Business Logic Attacks and Hidden Threats Expand Risk
Modern attackers are increasingly exploiting weaknesses in how financial systems operate rather than simply attacking technical vulnerabilities.
The report warns that payment systems, transaction limits and verification workflows can be manipulated through unusual sequences of legitimate actions. Attackers may abuse authorised functions in ways that developers never intended, making such activities difficult to detect.
It also highlights threats from fileless malware, encrypted communication channels and incomplete monitoring systems. These techniques can allow attackers to remain hidden while moving through networks or extracting sensitive information.
Report Calls for Continuous Cyber Defence Strategy
The assessment outlines several major security challenges expected to shape the future threat landscape, including AI-powered fraud, identity compromise, payment manipulation, supply-chain attacks and risks affecting critical financial infrastructure.
To address these challenges, the report recommends an 18-month security improvement roadmap focused on strengthening basic protections, expanding monitoring capabilities and redesigning security architecture.
The report concludes that cybersecurity must become an ongoing business priority for financial organisations. In an environment where cyberattacks can scale rapidly through automation and AI, periodic security checks are no longer enough. Continuous protection, testing and adaptation will be essential to maintaining trust and stability in the financial sector.






Patna Cyber Police have busted an alleged organised cybercrime racket involved in digital arrest scams, financial fraud and online cheating, arresting three accused. Police said the suspects allegedly targeted victims across several states and were linked to a wider cybercrime network.
During the operation, investigators recovered six mobile phones, two laptops, three cheque books, two passbooks and five ATM cards, along with other electronic devices and banking documents.
Three Accused Arrested
The arrested accused have been identified as Gaurav Kumar, a resident of New Colony in Khagaul-Danapur; Adarsh Kumar of Transport Nagar; and Aman Raj of Kumhrar. According to police, the three were allegedly connected to an organised cybercrime network operating across different parts of the country. Preliminary investigation also revealed multiple complaints related to cyber fraud against them.
Cybercrime Complaints Helped Trace Suspects
Police said several complaints concerning the accused were found on the National Cybercrime Reporting Portal. Analysis of these complaints, along with digital evidence collected during the investigation, helped investigators trace the suspects and establish their alleged links with the racket.
Technical surveillance and examination of digital evidence played a key role in the investigation. Investigators analysed suspected mobile numbers, electronic devices and other digital activities before identifying and tracing the accused. The seized mobile phones and laptops have now been sent for detailed examination to identify additional suspects, victims and possible financial transactions.
Phones, Laptops And Banking Documents Seized
Police suspect that bank accounts and documents recovered from the accused may have been used to receive and transfer money obtained through cyber fraud. The three cheque books, two passbooks and five ATM cards are being examined to establish the flow of funds and identify accounts allegedly linked to the racket. Investigators are also examining the electronic devices for communication records, transaction details and other digital evidence.
How Digital Arrest Scams Work
The investigation is also focused on determining how the accused allegedly carried out digital arrest scams. In such frauds, cybercriminals typically impersonate police officers, central investigation agencies, bank officials or other government authorities and threaten victims with arrest or legal action. The victims are then kept under constant pressure through phone or video calls and are allegedly persuaded to transfer money on the pretext of verification, investigation or avoiding arrest.
FIR Registered, Investigation Expanded
An FIR has been registered at Patna Cyber Police Station, and the investigation has been expanded to determine the complete structure of the alleged network. The three accused were produced before a court and remanded to judicial custody. Police are now examining the seized electronic devices and banking records to establish the roles played by the accused and identify other members of the network.
Investigators are also trying to determine the total amount allegedly siphoned off by the racket and the number of victims who may have been targeted. Since complaints have surfaced from different parts of the country, authorities are examining whether the suspects were operating independently or as part of a larger network involving multiple handlers, bank accounts and money-transfer channels.
Expert Warns Against Digital Arrest Scams
Cybercrime expert and former IPS officer Prof. Triveni Singh said digital arrest scams combine technology with psychological manipulation. Victims are often kept under intense pressure and made to believe that immediate action is required to avoid arrest or other legal consequences. People should independently verify any such claim through the official contact details of the concerned department and should never transfer money merely because someone threatens them with arrest over a phone or video call.
Patna Cyber Police said the investigation remains underway. Further action will follow after the roles of other suspected members are established. Investigators are also analysing the digital and banking evidence recovered during the operation to determine the actual scale of the alleged fraud, trace the money trail and identify additional victims and associates connected to the network.
The Delhi High Court has expressed serious concern over cases of fraudulent GST registrations obtained by misusing the PAN and Aadhaar details of unsuspecting citizens, giving the Centre and Delhi Police a final opportunity to devise an effective mechanism to prevent such fraud.The court observed that if the allegations made in the petitions are correct, fraudulent GST registrations are being obtained on a large scale in the names of innocent people, exposing them to substantial tax liabilities and causing revenue losses to the government.
Woman Alleges PAN-Aadhaar Misuse
A Bench of Justice Anil Khetarpal and Justice Shail Jain passed the order while hearing two petitions. One of the petitions was filed by a woman named Neha, who alleged that another person had used her PAN and Aadhaar details to obtain a fraudulent GST registration in her name.
The court noted that this was the second such case before it. The Bench observed that, if the allegations were found to be correct, they indicated that fraudulent GST registrations were being carried out extensively using the identities of innocent citizens. Such registrations can leave individuals facing tax liabilities arising from businesses with which they have no connection.
Court Suggests Facial Recognition And Video Verification
During the hearing, senior advocate Tarun Gulati placed several technological and administrative measures before the court to prevent misuse of PAN and Aadhaar details. One of the key suggestions was mandatory facial recognition of every GST registration applicant against the Aadhaar database.
The proposals also included video-based verification. Under the suggested system, an applicant would have to upload a 20-to-30-second video showing their face and the original PAN and Aadhaar cards. The applicant would also be required to read out a system-generated prompt containing their details and a unique code. The measure is intended to reduce the possibility of third parties using stolen or misused identity documents to obtain GST registrations.
IP Tracking And Physical Verification Proposed
Another proposal was to record and preserve the IP address and device location used while submitting a GST application. The information would remain available with the GST portal and the concerned jurisdictional authority so that it could be examined later if the identity of the person who submitted the application is disputed.
To identify shell or fraudulent businesses, the suggestions included mandatory physical verification of the proposed principal place of business before granting GST registration. Alternatively, a risk-based system could be used to conduct random physical inspections of GST-registered businesses twice a year.
Real-Time Alerts And Additional Safeguards
The proposals further called for real-time data sharing between the GST and Income Tax departments. Under such a system, a PAN holder could receive an immediate alert whenever their PAN is used to obtain GST registration. The system could also flag sudden and significant increases in turnover for further scrutiny.
Other proposed safeguards include alerts through DigiLocker, specific risk parameters for PAN-Aadhaar mismatches and additional checks when a PAN or Aadhaar number is being used for GST registration for the first time. Applicants could also be required to provide details of identifiable persons who can corroborate their identity and confirm the existence of the proposed business.
Centre And Police Given Final Chance
The Bench recorded that the respondents had not disputed that fraudulent GST registrations using the PAN and Aadhaar details of innocent citizens had become a serious problem since the implementation of the Central Goods and Services Tax Act, 2017. The court observed that nearly nine years had passed, yet authorities had failed to effectively curb the malpractice.
The court also expressed concern that an officer deputed by Delhi Police to assist it was unaware of the issue despite its seriousness. The Bench has now given the CGST Commissioner, DGST Commissioner and Delhi Police Commissioner a final opportunity to find an effective solution.
The court warned that if the authorities failed to take effective measures, it would have no option but to pass appropriate and effective orders. The matter has been listed for further hearing on September 8.
What Happens Next?
The Delhi High Court’s intervention puts the spotlight on the need for stronger safeguards against identity misuse in GST registrations. With the Centre and Delhi Police given a final opportunity to address the issue, the next hearing on September 8 is expected to indicate what measures authorities propose to prevent fraudulent registrations and protect innocent PAN-Aadhaar holders from wrongful tax liabilities.
Two Ahmedabad businessmen lost a combined ₹6.79 lakh after allegedly falling victim to a cyber fraud involving fake traffic e-memo messages. In separate incidents reported from Isanpur and Baherampura, fraudsters used vehicle numbers in messages to make the alerts appear genuine and allegedly gained access to the victims’ mobile phones after they opened the links.
How Did The Isanpur Businessman Lose ₹4.58 Lakh?
Kunal Batukbhai Prajapati, 38, who runs Kunal Infotech in Isanpur, received a message from an unknown number regarding a ₹1,000 traffic memo linked to vehicle number GJ27AP6801.
Prajapati clicked on the link included in the message but did not make any payment. Soon afterwards, his phone began receiving repeated OTP messages from different numbers.
Later that night, he received alerts about several transactions from his bank account. He discovered that ₹4.58 lakh had been withdrawn through six transactions.
What Happened After The Fraud Was Detected?
After realising what had happened, Prajapati switched off his mobile phone and contacted the 1930 cybercrime helpline. He subsequently filed a complaint at the Isanpur police station.
How Was A Baherampura Resident Duped Of ₹2.21 Lakh?
In the second incident, a 48-year-old Baherampura resident received a WhatsApp message from an unknown sender claiming that an e-challan was pending against his two-wheeler.
The message contained his vehicle number and a link related to the alleged challan. When he opened the link, an application was downloaded onto his phone.
How Did The Fraudsters Gain Access To The Bank Account?
The man realised something was wrong only after receiving bank transaction alerts the following day. On checking his account, he found that ₹2.21 lakh had been taken out through multiple transactions.
The complaint alleges that the application gave the fraudsters access to the mobile phone, after which they carried out unauthorised transactions.
How Does The Fake E-Memo Scam Work?
The fraud begins with a message designed to look like an official traffic notice. Fraudsters use a vehicle owner’s registration number and claim that a fine, often for ₹500 or ₹1,000, remains unpaid.
The message contains a link directing the recipient to supposedly clear the fine. Instead of making a legitimate payment, victims may be prompted to download an APK application.
Once installed, such an application can potentially gain access to SMS messages and other information on the device. This can allow criminals to obtain sensitive banking information, including OTPs, and carry out transactions without the victim immediately noticing.
Both Ahmedabad cases were reported after the victims noticed unauthorised withdrawals. They contacted 1930, the cybercrime helpline, and approached the respective police stations.
What Should Vehicle Owners Do After Receiving Such Messages?
Cyber crime experts have urged citizens to be cautious about traffic fine messages received from unknown numbers and to avoid opening suspicious links or installing applications sent through such messages.
-
 Business3 years ago
Pot Odor Does Not Justify Probable Cause for Vehicle Searches, Minnesota Court Affirms
-
 Business3 years ago
New Mexico cannabis operator fined, loses license for alleged BioTrack fraud
-
 Business3 years ago
Alabama to make another attempt Dec. 1 to award medical cannabis licenses
-
 Business3 years ago
Washington State Pays Out $9.4 Million in Refunds Relating to Drug Convictions
-
 Business3 years ago
Marijuana companies suing US attorney general in federal prohibition challenge
-
 Business3 years ago
Legal Marijuana Handed A Nothing Burger From NY State
-
 Business3 years ago
Can Cannabis Help Seasonal Depression
-
 Blogs3 years ago
Cannabis Art Is Flourishing On Etsy