
AICybercrime
₹657 Crore Haryana Bank Scam: CBI Flags 47 Debit Alerts Sent to Co-Accused

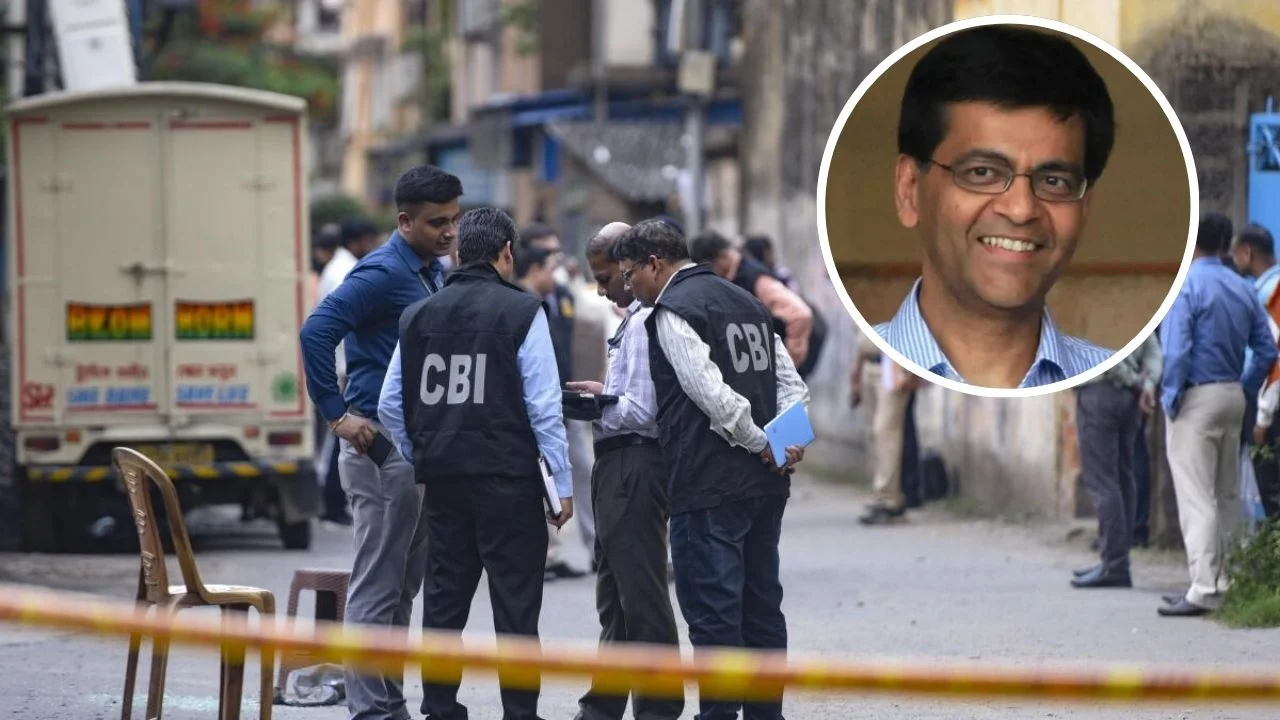
The Central Bureau of Investigation (CBI) has uncovered critical digital evidence in the ongoing probe into the alleged ₹657 crore Haryana bank fraud, revealing that SMS alerts linked to dozens of suspicious transactions were allegedly diverted to mobile numbers controlled by individuals connected to the accused.
The findings were presented before a court in Panchkula, where two former bank officials were remanded to CBI custody as investigators expand their probe into what appears to be a deeply coordinated banking and financial manipulation network.
Fraud Alerts Routed to Unauthorized Numbers
According to the CBI, 47 suspicious debit transactions worth approximately ₹187.26 crore triggered SMS alerts that were not delivered to authorized government officials. Instead, the alerts allegedly reached mobile numbers linked to co-accused individuals.
Investigators believe this diversion played a crucial role in concealing unauthorized withdrawals from multiple government department accounts.
Bank Officials Under Scrutiny
The court has sent former IDFC First Bank Area Head Shamim Dar and former AU Small Finance Bank Branch Manager Charanjeet Singh Randhawa to three days of CBI custody.
The agency alleges that Dar played a key role in facilitating the opening of several government-linked accounts at a Chandigarh branch by certifying Know Your Customer (KYC) documents and confirming account verification procedures that are now under question.
These certifications, investigators claim, were later exploited to operate accounts using allegedly forged or manipulated banking instruments.
Suspicious Account Activity Across Departments
The investigation has revealed that multiple government accounts, including those belonging to the Haryana State Pollution Control Board (HSPCB), Haryana School Shiksha Pariyojna Parishad (HSSPP), and Haryana State Agricultural Marketing Board (HSAMB), were allegedly misused for fraudulent financial transactions.
One mobile number linked to a co-accused, Abhishek Singla, was reportedly registered across multiple government accounts and used to receive transaction alerts, raising concerns over systemic security failures in account verification processes.
Alleged Fake Vendor Payments and High-Value Transfers
The CBI has also flagged several transactions presented as legitimate payments to vendors or contractors, which investigators now suspect were used to bypass internal financial approvals.
Among the flagged activities is a ₹2.49 crore transaction categorized as a vendor payment and a ₹10 crore withdrawal executed using a cancelled cheque. Officials allege that procedural checks were bypassed or manipulated to enable these transfers.
Shell Company and Large-Scale Fund Diversion
Investigators have identified a firm named M/s Swastik Desh Projects, which is suspected to be a shell entity used for routing fraudulent transactions.
According to the agency, multiple payments from the Panchayat Department account were transferred to this entity, including transactions allegedly linked to former bank officials involved in authorization and verification processes.
The CBI also highlighted a ₹25 crore transaction from the HPGCL Employees’ Pension Fund Trust account that was allegedly diverted to the same entity on December 29, 2025.
Probe Focus: Digital Evidence and Money Trail
The investigation is now centered on analyzing call detail records, banking documentation, KYC verification files, and digital transaction logs to reconstruct the complete flow of funds.
Authorities are also examining whether unauthorized changes were made to registered mobile numbers in government accounts, which may have enabled the concealment of fraudulent activity.
Systemic Lapses Under Review
Officials say the case has raised serious concerns about banking compliance, verification procedures, and oversight mechanisms in handling government-linked accounts.
The CBI is currently working to establish the full extent of involvement of all accused individuals while assessing whether the fraud was part of a larger organized financial network



Cyber fraud is no longer limited to phone calls, messages or fraudulent links. The Indian Cyber Crime Coordination Centre (I4C) has warned Android users about malicious applications being promoted on social media platforms such as Facebook and Instagram by disguising them as adult-content apps.
Users who click on these advertisements are redirected to external websites and persuaded to download APK files from outside the Google Play Store. Once installed, the apps can seek sensitive permissions and attempt to gain access to the device and personal information.
Which Fake Apps Has I4C Flagged?
The I4C, which operates under the Ministry of Home Affairs, has flagged suspicious applications operating under names such as “Night Play”, “Reloop”, “Kyss”, “Vimo”, “Rivo”, “Nexo” and “Vixa”, among others.
These apps are reportedly promoted through social media advertisements offering users access to adult content. Clicking on the advertisements takes users to websites where they are instructed to download an application to view the content.
How Does the APK Fraud Begin?
The fraud begins when users are persuaded to install an APK file from an external website instead of downloading an application through the Google Play Store. After installation, the malicious application may request access to sensitive functions such as notifications, messages or other device features. The risk becomes particularly serious when users grant an unfamiliar application access to Android’s Accessibility Services.
Why Is Accessibility Permission So Dangerous?
Accessibility Services is designed primarily to assist people who have difficulty operating touchscreen devices. However, cybercriminals can misuse this functionality. According to cybersecurity experts, a malicious application with Accessibility access may be able to read information displayed on the screen, interact with other applications and potentially approve certain permission requests on behalf of the user.
This creates a direct threat to banking and digital payment information. Smartphones often contain banking applications, UPI accounts, one-time passwords (OTPs), private messages and other sensitive information. If a malicious application gains extensive control over such a device, attackers may potentially exploit that access to facilitate financial fraud.
Some variants of the malware may also download another package by disguising it as an application update. In certain cases, the malicious software may install a VPN and attempt to route internet traffic through servers controlled by attackers. Such activity can further compromise the security and privacy of an affected device.
What Warning Signs Should Android Users Watch For?
Cybersecurity experts have advised users to pay close attention to unusual activity after installing an unfamiliar application. A phone appearing to tap or interact on its own, an unfamiliar VPN icon appearing on the device, or an unknown application showing up under Accessibility settings could be warning signs of a possible compromise.
Experts have also warned that users may be more likely to trust advertisements appearing on familiar social media platforms. However, being redirected from a legitimate platform to an external website and then being asked to install an APK significantly increases the security risk. Cybercriminals are increasingly targeting users before a financial transaction takes place, using deceptive advertisements and applications to gain access to devices and sensitive information.
The I4C has advised Android users to download applications only from the Google Play Store or other trusted app stores. Users should avoid APK files received through advertisements, websites or suspicious links. They should also keep Google Play Protect enabled, regularly update their Android devices and periodically review the applications installed on their phones.
Users should immediately review and remove applications they do not recognise and avoid granting Accessibility access to unfamiliar applications. Particular caution is required when an application asks users to enable unusual permissions or follow instructions to bypass normal installation procedures.
Users should also regularly monitor their bank accounts and UPI transactions for unauthorised activity. If someone suspects that their device has been infected with malware or notices an unauthorised financial transaction, they should immediately contact their bank and report the incident through India’s cybercrime helpline at 1930.
The threat also extends beyond personal smartphones. Employees may use the same devices for work email, banking and personal activities, potentially exposing organisational information to malicious applications. Companies should therefore consider restricting app installation from external sources on devices that access sensitive corporate data and maintain a response plan for suspected compromises.
The latest warning highlights a simple but critical cybersecurity rule: users should never install an unfamiliar application merely because an online advertisement promises free or exclusive content. Downloading apps from trusted sources and carefully reviewing requested permissions can significantly reduce the risk of handing control of a smartphone to cybercriminals.
Police in Maharashtra have registered a cheating case against a retired Army officer and his associate for allegedly duping a man of ₹11 lakh by falsely promising to secure a government job for his son. Investigators claim the accused staged a fake recruitment process, including a mock interview and forged official documents, before offering an alternative government position when the original promise failed.
Victim Allegedly Lured With Promise of Income Tax Department Job
According to the police complaint, Yusuf Lotan Pinjari, an RTO agent from Ulhasnagar, was searching for a government job opportunity for his commerce graduate son. During this time, a relative introduced him to Bharat Ashok Devre, a resident of Nashik and a retired Army officer who allegedly claimed to have influence in government recruitment.
Police said Devre allegedly assured the family that vacancies linked to the 2023 waiting list in the Income Tax Department were being filled and that he could arrange an appointment. Investigators allege he demanded a total of ₹16 lakh for the recruitment process, requesting an advance payment to begin the procedure.
Believing the assurances, the complainant allegedly paid ₹4 lakh initially. Authorities say additional payments were sought later after the accused claimed that educational certificates had been verified and the selection process had progressed.
Fake Interview and Forged Documents Under Investigation
As per the complaint, Pinjari was later instructed to travel to Aurangabad with another ₹5 lakh. At a hotel, he reportedly met Baban Bhausaheb Gaikwad and another individual who was allegedly introduced as an Income Tax Department employee.
Investigators claim the complainant’s son was made to participate in what appeared to be an official interview, submit educational documents, and receive paperwork purportedly related to a government medical examination. During the meeting, another ₹5 lakh was allegedly handed over to the accused.
Despite these developments, no appointment letter was issued.
Alternative Job Offer Raised Further Suspicion
Police said that when the promised Income Tax Department job failed to materialize, the accused allegedly informed the complainant that they could instead secure employment in the Nashik Health Department.
To support this claim, they reportedly shared a waiting list showing the complainant’s son at serial number 65. The complainant later alleged that the document was fabricated and intended only to create the impression that the recruitment process was ongoing.
After several months without any appointment in either department, Pinjari approached the police, alleging he had been deceived.
Police Probe Financial Trail and Possible Wider Fraud
Based on the complaint, Mahatma Phule Police Station has registered a case against Bharat Ashok Devre and Baban Bhausaheb Gaikwad under relevant provisions of the Bharatiya Nyaya Sanhita (BNS) for alleged cheating.
Investigators are examining the financial transactions, verifying the authenticity of the documents presented to the complainant, and reviewing the circumstances surrounding the alleged interview. Police are also exploring whether the accused may have used a similar method to target other job seekers.
Authorities have urged citizens to avoid paying money to anyone claiming they can guarantee government employment and to verify all recruitment announcements through official government channels before making any financial commitments.
Police in Punjab’s Moga district have registered a case against three employees of Annapurna Finance Private Limited for allegedly misappropriating ₹11.70 lakh from the company’s Ajitwal branch. The accused have been booked after an internal inquiry and a preliminary investigation reportedly found evidence supporting allegations of document forgery and financial misconduct.
Internal Audit Reveals Suspicious Transactions
According to police officials, the complaint was filed by Pragat Singh, the company’s Area Manager, who oversees operations of eight branches, including the Ajitwal unit.
The alleged irregularities came to light during routine monitoring and verification of financial records. Following the detection of suspicious transactions, the company conducted an internal review to examine possible discrepancies in branch accounts.
The complaint alleged that employees posted at the Ajitwal branch — identified as Kuldeep Singh, Nachhattar Singh, and Robin — were involved in preparing false documents, creating inaccurate records, and manipulating financial entries.
Investigation Finds Prima Facie Evidence
Due to the seriousness of the allegations, the matter was referred to the Deputy Superintendent of Police (Special Crime) for further examination.
During the inquiry, investigators reviewed banking details, branch records, financial documents, and transaction-related evidence. The preliminary findings reportedly indicated that the allegations had sufficient basis for registration of a criminal case.
Following the inquiry report, Ajitwal Police registered an FIR against the three accused under relevant provisions of the Bharatiya Nyaya Sanhita (BNS) related to cheating, forgery, criminal breach of trust, and other offences.
Police Examine Money Trail and Possible Involvement of Others
Authorities said the investigation is ongoing and teams are examining the movement of the allegedly diverted funds. Police are working to identify the accounts that may have received the money and determine whether additional individuals were involved.
Investigators are also analyzing digital transaction records, banking trails, and company documents to establish the complete nature of the alleged financial irregularities.
The probe will further examine whether gaps in internal controls or monitoring systems were exploited to carry out the suspected fraud. If evidence reveals the involvement of additional persons, further legal action may follow.
Experts Highlight Need for Stronger Internal Controls
Financial security experts have emphasized the importance of strict internal audit procedures, employee verification systems, transaction monitoring, and multi-level approval processes to prevent insider fraud in financial organizations.
They recommend that financial institutions adopt stronger safeguards, including separation of duties, regular independent audits, risk-based monitoring, and improved digital transaction oversight.
Such measures can help detect suspicious activities at an early stage, reduce financial losses, and improve transparency within organizations.
Meanwhile, Moga Police continue their investigation into the alleged embezzlement case, with further action expected based on the evidence collected.
-
 Business3 years ago
Pot Odor Does Not Justify Probable Cause for Vehicle Searches, Minnesota Court Affirms
-
 Business3 years ago
New Mexico cannabis operator fined, loses license for alleged BioTrack fraud
-
 Business3 years ago
Alabama to make another attempt Dec. 1 to award medical cannabis licenses
-
 Business3 years ago
Washington State Pays Out $9.4 Million in Refunds Relating to Drug Convictions
-
 Business3 years ago
Marijuana companies suing US attorney general in federal prohibition challenge
-
 Business3 years ago
Legal Marijuana Handed A Nothing Burger From NY State
-
 Business3 years ago
Can Cannabis Help Seasonal Depression
-
 Blogs3 years ago
Cannabis Art Is Flourishing On Etsy